
How DGI cut security admin time by 60% for a global iGaming business with Cato SASE
Connecting employees and new offices had become an operational constraint for a global iGaming business. Its existing OpenVPN setup limited access controls, slowed development workflows, and left gaps in visibility across cloud applications.
DGI Tech Group implemented Cato Networks’ SASE platform, which brings networking and security together, in three weeks, including configuration, testing, and training. The client reduced security administration time by 60% and can now connect a new office in one day.
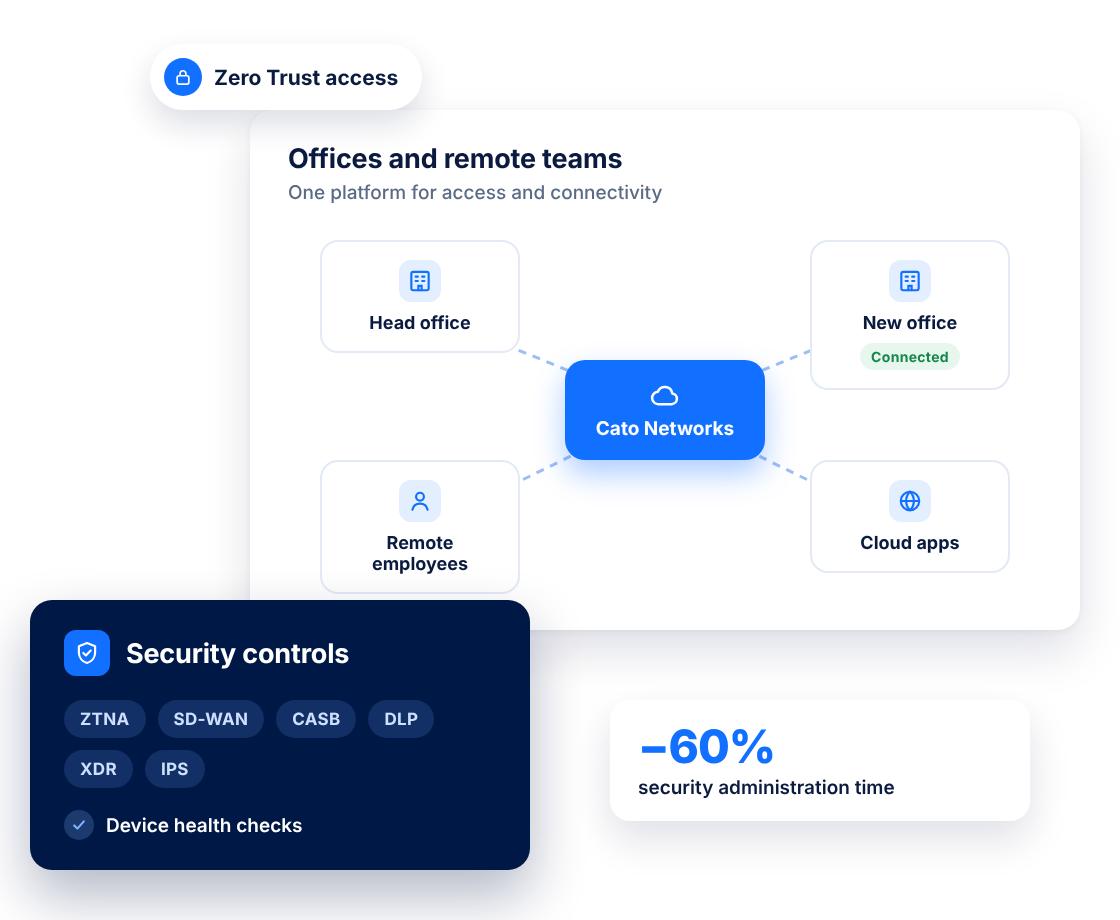
Project at a glance
Client
A global online gaming and gambling business.Scale
250+ employees and 10M+ monthly active users.Solution
Cato Networks for secure access, networking, and security.Deployment
Three weeks, including setup, testing, and training.
Access and connectivity struggled to keep pace with growth
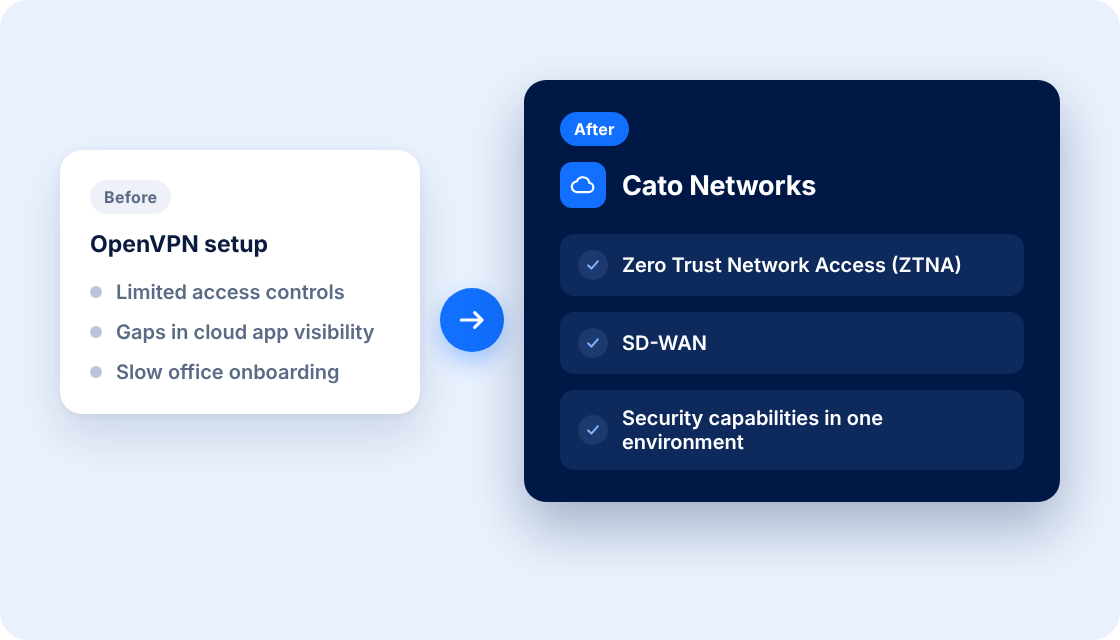
The client’s existing OpenVPN implementation no longer met its requirements for access control and visibility into cloud application use. Development workflows were affected, and bringing new locations online was slow and inefficient.
The business needed stronger controls in an environment that was easier for its technical team to manage. The rollout addressed both security requirements and the operational work involved in supporting employees and locations.
How DGI delivered the Cato Networks rollout
Bringing access and networking onto one platform
DGI introduced Cato Networks, including Zero Trust Network Access (ZTNA) and SD-WAN. The implementation brought access, connectivity, and the selected security capabilities into a common environment.
Configuring controls for devices, applications, and data
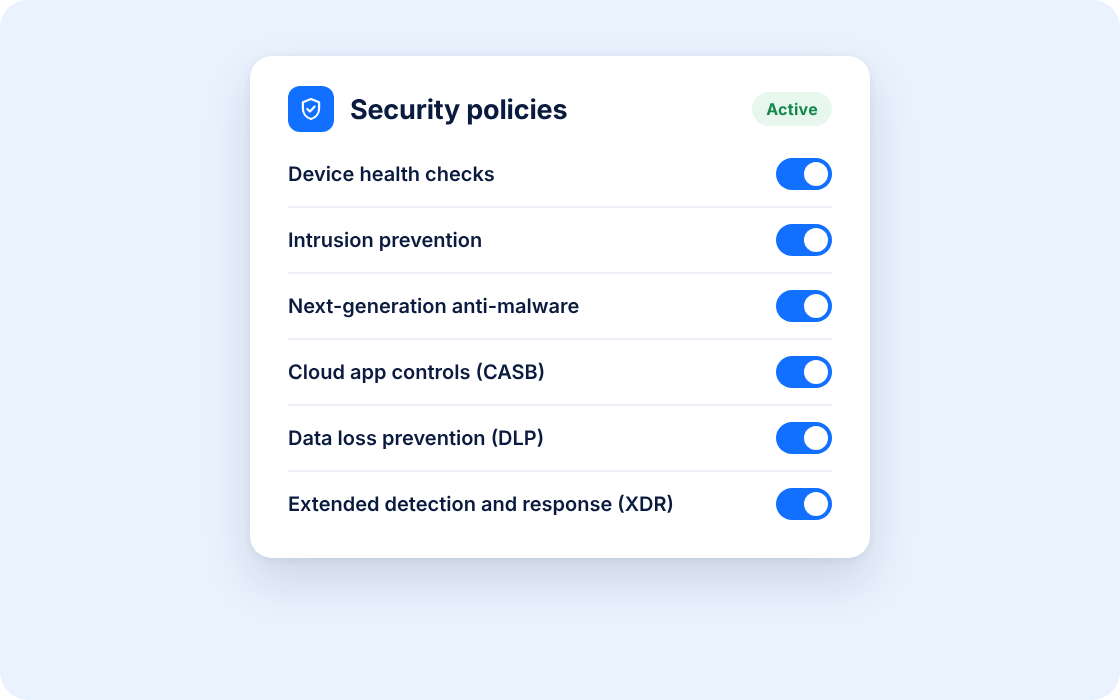
The deployment included device health checks, intrusion prevention, next-generation anti-malware, cloud application controls (CASB), data loss prevention (DLP), and extended detection and response (XDR).
This scope addressed the client’s access-control requirements and gaps in cloud application visibility, alongside threat protection and data controls.
Completing setup, testing, and training in three weeks
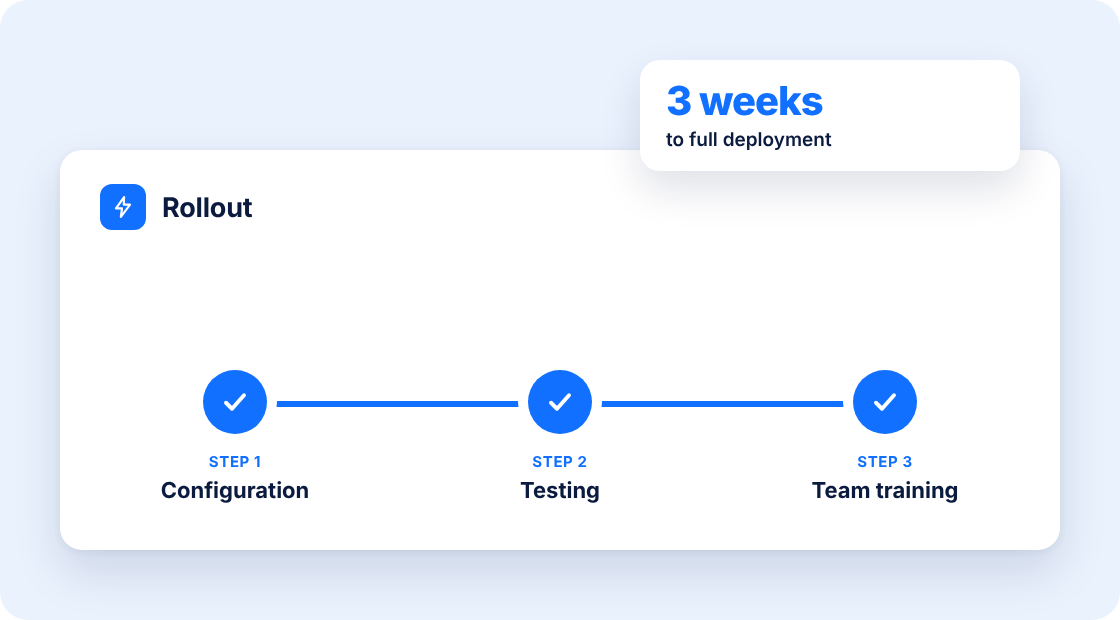
The three-week rollout included configuration, testing, and team training. DGI’s work covered bringing the platform into operation and preparing the team to use it.
Less administration and faster office connectivity setup
-
3 weeks
to full deployment, including setup, testing, and training
-
60%
less time spent on security administration
-
1 day
to connect a new office
-
Less administration, faster expansion
The technical team spent less time on security administration. The new platform also gave the company a faster way to connect additional offices, addressing a constraint that had made expansion inefficient.
Questions about this Cato Networks implementation
-
The client’s existing configuration created access-control limitations, gaps in cloud application visibility, and friction in development workflows. Connecting new locations was also slow.
-
The deployment included configuration, testing, and training. Its scope covered ZTNA, device health checks, threat protection, CASB, DLP, XDR, and SD-WAN.
-
The client can now connect a new office in one day, addressing the slow onboarding of new locations described at the start of the project.
Is managing access taking too much of your team’s time?
Tell DGI where employees encounter access problems and which tasks create the most work for IT. We can help review your current setup and assess an approach that fits your security requirements and plans for growth.