
€120K in monthly profit protected: stronger iGaming security with DGI and Cloudflare
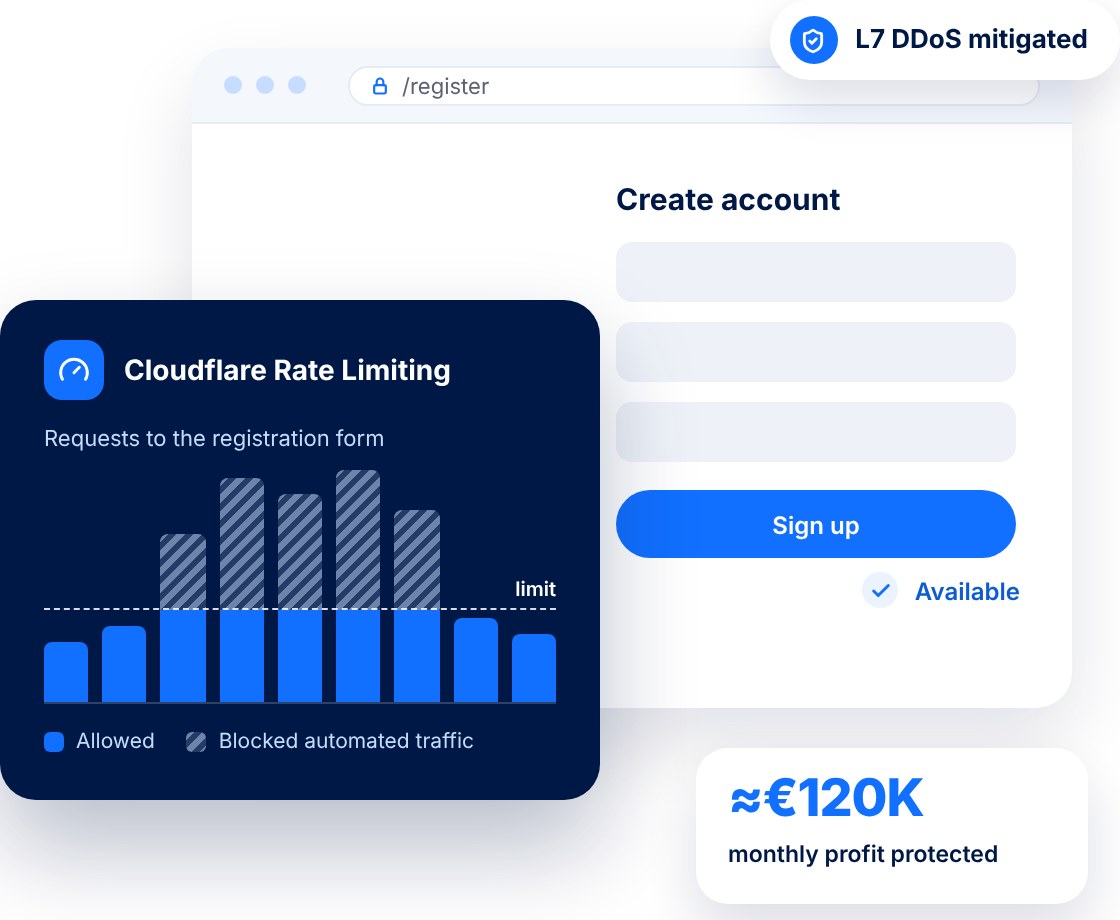
A Cloudflare security audit by DGI Tech Group uncovered a gap in a European gaming operator’s protection: its registration form lacked the request-rate controls needed to withstand automated abuse.
When an application-layer DDoS attack targeted that gap, DGI helped the operator’s technical team configure Cloudflare Rate Limiting and mitigate it. The additional protection eliminated recurring attack-related disruption, protecting approximately €120,000 in monthly profit and paying for itself in less than a month.
Client
An established European B2C gaming operator.
Several thousand employees across multiple offices and land-based gaming venues.
Physical casinos alongside an expanding online gaming business.
A regulated environment with strong requirements for security and service availability.
Background
The operator had used Cloudflare’s free and lower-tier services for years. As its online business grew, it moved to Enterprise services and needed specialist input on its security requirements.
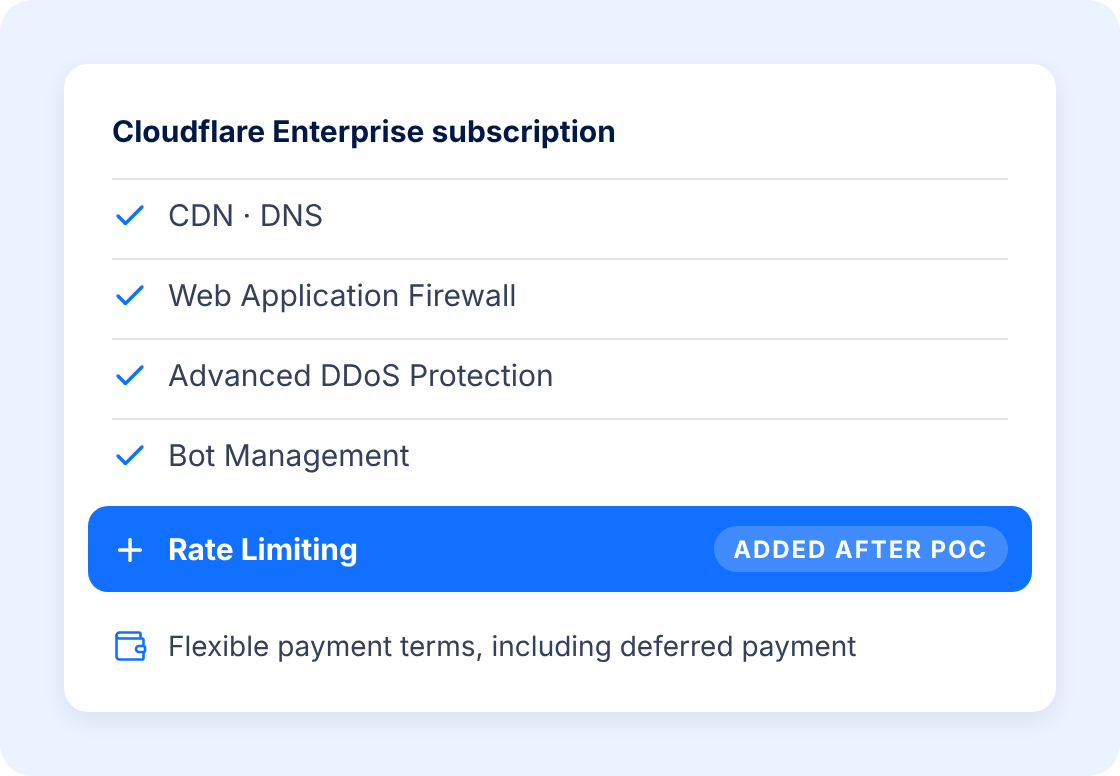
Cloudflare introduced DGI for its iGaming experience. DGI helped assess relevant threats, define subscription options and agree commercial terms. The approved package included CDN, DNS, Web Application Firewall (WAF), Advanced DDoS Protection and Bot Management. Rate Limiting remained outside the initial budget.
The client’s internal team configured and tested the services, then carried the setup into production. It asked DGI for an independent configuration review to understand where further adjustments or protection were needed.
Challenges
-
Business losses from service disruption
Attack-related interruptions affected access to the online platform. At an estimated profit impact of €30,000 per hour, even short incidents had material consequences.
-
Uncertainty about protection in practice
The operator needed to establish whether its Enterprise services and configuration adequately protected critical functions, including registration.
-
A clear case for additional investment
The technical team needed to connect further security spending to a specific business risk and demonstrate that the proposed solution would address it.
What DGI did
1. Audited the Cloudflare production configuration
DGI conducted a complimentary review and documented 50 findings of varying severity, identifying configuration issues and gaps in protection.
2. Identified the registration form’s exposure
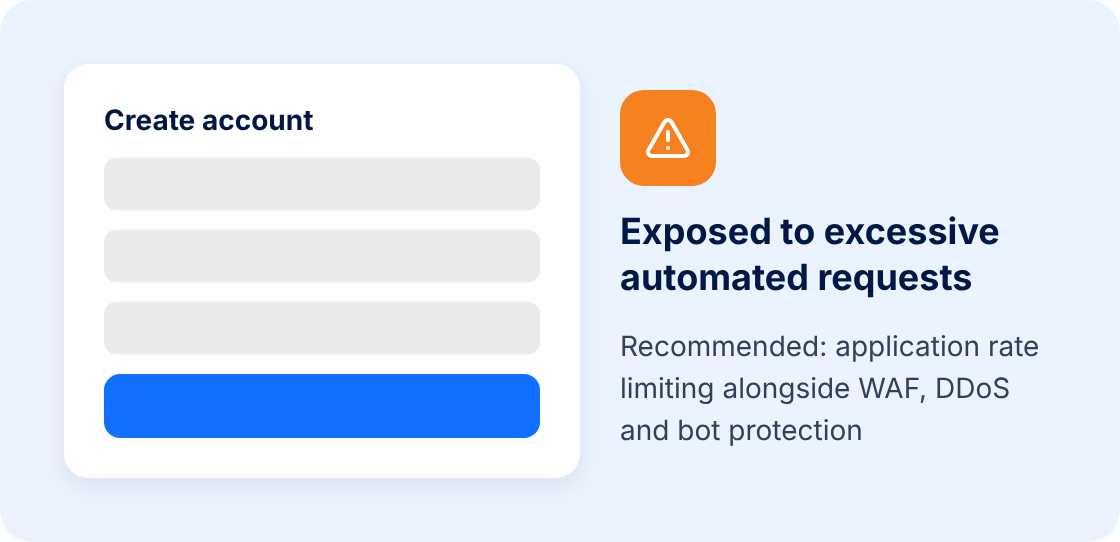
The audit found that the form needed targeted controls against excessive automated requests. DGI recommended application rate limiting alongside the existing WAF, DDoS and bot protection.
3. Helped mitigate an application-layer DDoS attack
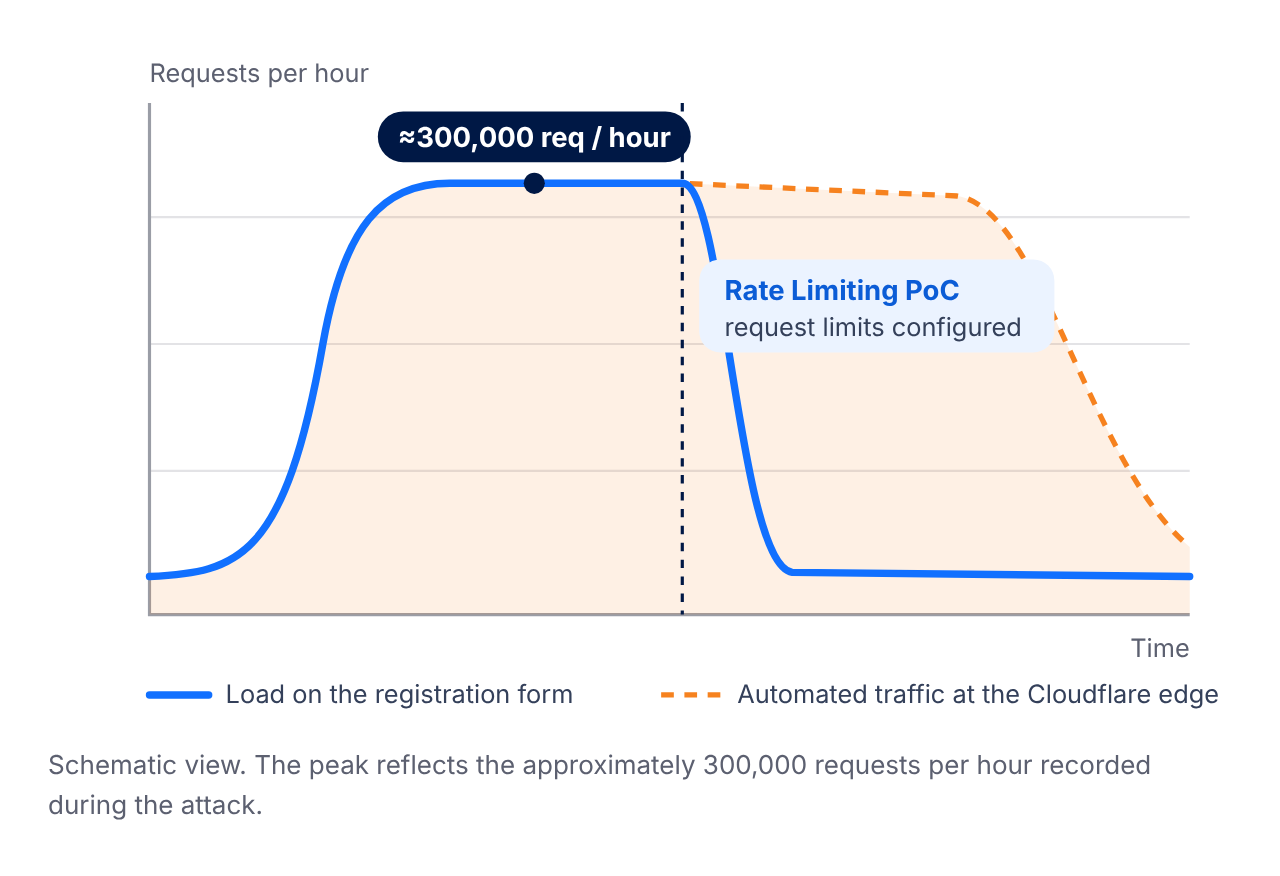
An application-layer DDoS attack (L7) then targeted the registration form with approximately 300,000 requests per hour. Cloudflare enabled Rate Limiting for a free proof of concept, and DGI guided the client’s team in configuring request limits to reduce the load from automated traffic. The team applied the settings and successfully mitigated the attack.
4. Extended the production subscription
Following the successful PoC, the operator purchased Rate Limiting for ongoing use. DGI supported the subscription expansion and offered flexible payment terms, including deferred payment.
Results
-
≈€120K
protected monthly
Estimated profit losses avoided by eliminating recurring attack-related disruption.
-
<1 month
to payback
Avoided losses covered the security investment in under a month.
-
≈4 hours
recovered monthly
Recurring service interruptions eliminated, keeping the online platform available to customers.
-
0
repeat disruptions
No further attack-related service interruptions recorded during the three-month follow-up period.
-
Clear security priorities
The internal team gained a clear view of protection gaps and the changes needed, helping focus effort and budget where it mattered most.
Why the client chose DGI Tech Group
Cloudflare expertise grounded in iGaming
DGI combines experience across dozens of iGaming projects with Cloudflare Powered+ partner status and Application Security Service Specialization. That expertise helped identify a specific exposure and recommend the capability needed to address it.
Practical support beyond the subscription
DGI reviewed the live configuration and guided the internal team when the identified gap was targeted. Support continued beyond product selection and purchase.
Validation before additional commitment
The Rate Limiting PoC demonstrated that the recommendation could mitigate the attack before the operator committed to purchasing it.
Technical and commercial decisions handled together
DGI helped align the required protection with subscription scope, budget and payment terms. The client worked with one partner for both technical guidance and purchasing support.
Questions about this Cloudflare security case
-
The registration form needed targeted limits on request frequency to reduce the load from excessive automated traffic. In this case, Cloudflare Rate Limiting provided the additional control required to mitigate the application-layer attack.
-
The production configuration review documented 50 findings of varying severity. One was a gap in registration-form protection, which DGI recommended addressing with application rate limiting before an attack targeted it.
-
The estimate combines approximately four hours of recurring service disruption per month with a profit impact of €30,000 per hour. Eliminating those interruptions avoided an estimated €120,000 in monthly profit losses. No further attack-related interruptions were recorded during the three-month follow-up period.
Find the gaps before they cost you
Could gaps in your application security put your business at risk? Get a free audit from DGI—whether you use Cloudflare or another solution.
Our specialists will review your current protection, identify gaps and recommend practical improvements to help prevent service disruption and business losses.